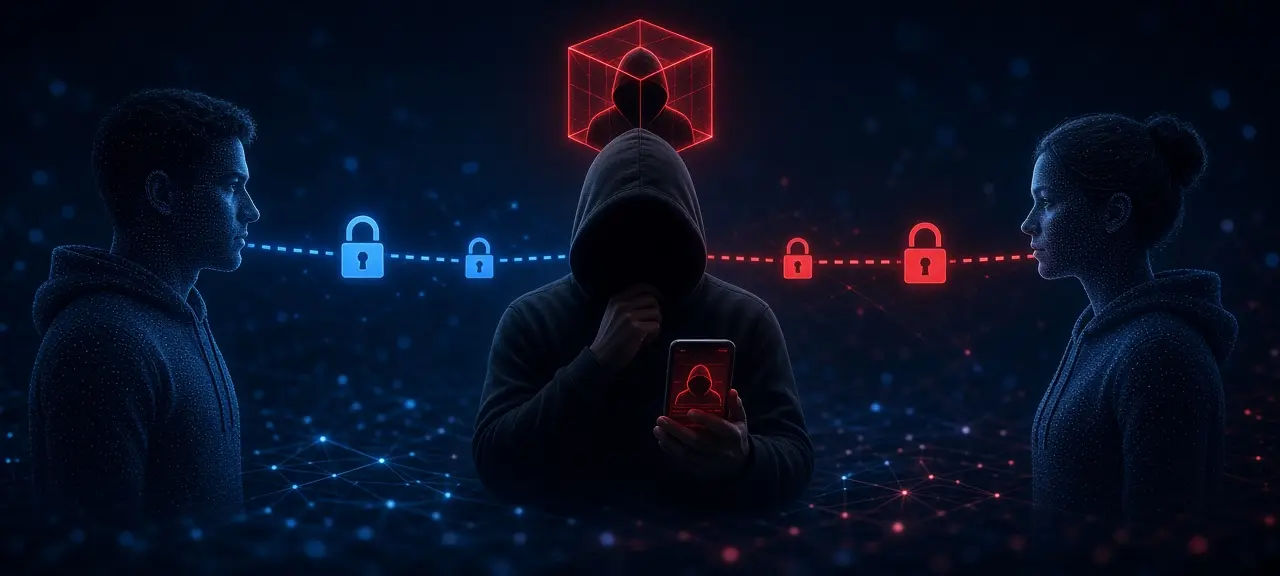
The short answer to what is a man in the middle attack: an attacker secretly sits between two parties, such as you and your bank's website, and intercepts or changes the data passing between them. NIST's glossary puts it as an attack in which the attacker "is positioned between two communicating parties in order to intercept and/or alter data traveling between them." Other names for a man-in-the-middle (MITM) attack are on-path attack, adversary-in-the-middle and, at OWASP, manipulator-in-the-middle. HTTPS blocks most of these attacks today. So modern attacks aim at the moments HTTPS gets bypassed: when you click past a certificate warning, or type a one-time code into the wrong page.
How a man-in-the-middle attack works
A man-in-the-middle attack works in two stages. First the attacker gets into the path of your traffic, through a fake Wi-Fi hotspot, a device on your local network or a false DNS answer. Then the attacker reads or changes the data, or relays it untouched so the connection looks normal to both you and the website.
In a normal connection, your device reaches the website through your router and your internet provider. An attacked connection has one extra stop, the attacker's device, and neither side sees it.
A typical case: a café has two networks named "Cafe_Free_WiFi". One belongs to the shop, the other to a stranger at a corner table. If your laptop joins the wrong one, every request passes through the stranger's device first. On a site that uses HTTPS correctly, the stranger sees the domain you visit, but the page content and your password stay encrypted. Click through a certificate warning, though, and that protection is gone.
Types of man-in-the-middle attacks
Man-in-the-middle attacks differ mainly by where the attacker sits: on a fake hotspot, on your local network, inside DNS answers, between you and an HTTPS site, inside a logged-in session or a mailbox, behind a fake login page, or on a fake mobile tower.
| Type | Where the attacker sits | What they go after | Main defense |
|---|---|---|---|
| Evil twin Wi-Fi | A fake hotspot with a familiar name | Logins on unencrypted pages, fake sign-in portals | Confirm the network name with staff; mobile data |
| ARP spoofing | The same local network or shared Wi-Fi | Routing other devices' traffic through their own machine | HTTPS; guest Wi-Fi that isolates devices from each other |
| DNS spoofing | DNS answers | Sending you to a look-alike site | Check the domain and certificate; a trusted DNS resolver |
| SSL stripping (HTTPS spoofing) | Between you and the site | Downgrading to plain HTTP or a fake certificate | HSTS; never click through certificate warnings |
| Session hijacking | After you sign in | The session cookie that keeps you logged in | HTTPS on every page; sign out on shared devices |
| Email hijacking | Inside a compromised mailbox | Invoices, where the bank details get swapped | Confirm payment details by phone on a known number |
| Adversary-in-the-middle phishing | A fake login page that relays to the real one | Password, one-time code and session cookie | Passkeys or security keys |
| Fake mobile base station | A 2G radio near the victim | Spoofed text messages | 4G or 5G; turn off 2G if the phone allows it |
ARP spoofing works because of how the protocol is built. ARP (Address Resolution Protocol) maps IP addresses to hardware MAC addresses on a local network and has no built-in authentication. Any device on it can answer "that IP is me." DNS spoofing is a false answer to "where is this domain?" The guide to what DNS is and how lookups work covers the normal process.
Adversary-in-the-middle phishing is the type most people meet today. The fake page passes what you type to the real site in real time, so your one-time code works for the attacker too. Passkeys and FIDO security keys are tied to the real domain and won't sign in on a look-alike one. The difference between code-based and key-based sign-in is explained in two-factor vs two-step verification.
Real-world man-in-the-middle attack examples
Two documented cases show how HTTPS protection was bypassed at scale. In the 2011 DigiNotar breach, a trusted certificate authority issued forged certificates. In the Lenovo case, software preinstalled on laptops swapped website certificates for its own.
DigiNotar was a Dutch certificate authority. Attackers broke in and issued rogue certificates, one of them a wildcard certificate for google.com. Fox-IT's investigation report "Black Tulip" (version 1.0, August 13, 2012) lists 531 rogue certificates. It counts 298,140 unique IP addresses as victims of the MITM attack that used the google.com certificate, and 95% of them came from Iran. Fox-IT calls that count a rough estimate. The google.com certificate was revoked on August 29, 2011.
The FTC announced its settlement with Lenovo on September 5, 2017. From August 2014, Lenovo sold US consumer laptops with preinstalled ad software called VisualDiscovery. According to the FTC, it "acted as a 'man-in-the-middle' between consumers' browsers and the websites they visited." To show ads on HTTPS pages, it replaced the sites' certificates with its own. Lenovo must now get consent before preinstalling such software and run an audited software security program for 20 years.
Does HTTPS stop man-in-the-middle attacks?
Yes, in most cases. HTTPS encrypts page content with TLS, and the site's certificate proves the server controls the domain in the address bar. A man in the middle on an HTTPS connection can see which domain you reach, but can't read or change the content without the browser showing a certificate warning. Which versions still count as safe is covered in our guide to SSL/TLS protocols.
The attack works when that check is skipped. You click through a warning, a network asks you to install its own certificate or profile, or a site still serves some pages over plain HTTP. HSTS (HTTP Strict Transport Security, defined in RFC 6797 in 2012) closes that last gap. A site that sends the HSTS header tells your browser to use only HTTPS for that domain from then on, so an attempt to strip the connection down to HTTP fails.
Some companies and schools inspect HTTPS traffic on devices they manage by installing their own root certificate. That is a disclosed MITM inside one organization. A personal phone should not carry a root certificate you don't recognize.
Warning signs of a man-in-the-middle attack
The clearest warning signs are a certificate warning on a site you use every day, a familiar site loading without HTTPS, and a Wi-Fi network that asks you to install a certificate or profile. Many attacks show none of these signs. That is why prevention matters more than detection.
- A "connection is not private" warning on a site that never showed one.
- A site you know uses HTTPS suddenly loads as plain HTTP, with no padlock.
- A public Wi-Fi network asks you to install a certificate, a configuration profile or an app before you can browse.
- Two networks with the same name in one place.
- A login page asks for a one-time code when you didn't just start a sign-in.
- A sign-in alert from your email or bank showing an IP address or city you don't recognize.
No website, CheckIP included, can tell from your IP address whether someone is intercepting your connection.
How to prevent a man-in-the-middle attack
To stop a man in the middle attack, keep attackers off your path and keep HTTPS checks intact. Confirm Wi-Fi names before joining, never click through certificate warnings, use mobile data for banking on public networks, lock down your home router, and use passkeys or security keys on important accounts.
On public Wi-Fi and your phone
- Ask staff for the exact network name and password before you join.
- Don't press "Proceed" or "Accept the risk" on a certificate warning. Close the tab instead.
- Use mobile data instead of public Wi-Fi for banking and payments.
- Turn off auto-join for open networks, so the phone doesn't connect to a look-alike name by itself.
- Turn off 2G if your phone has that option. Some Android phones show an "Allow 2G" switch in mobile network settings.
On your home network
Change the router's admin password and the Wi-Fi password from the defaults, and use WPA2 or WPA3 encryption. Install firmware updates and turn off remote management if you don't use it. Every few weeks, see who is on your Wi-Fi: an attacker has to be on your network before ARP spoofing can work.
If you run a website
Serve every page over HTTPS, redirect HTTP to it and send the HSTS header. Mark session cookies Secure and HttpOnly, so they never travel over plain HTTP and page scripts can't read them. Remove mixed content, such as images still loaded over HTTP.
Does a VPN protect against man-in-the-middle attacks?
A VPN protects the stretch between your device and the VPN server, so an attacker on the same public Wi-Fi sees only encrypted traffic going to one server. It doesn't stop a phishing page and doesn't protect anything past the VPN server. The VPN provider becomes the new party in the middle.
Before you use a café network, check your current IP with the VPN on. The IP and ISP shown should belong to the VPN provider, not the café's provider. Leak tests are in the guide on how a VPN hides your IP.
Frequently asked questions
Is a man-in-the-middle attack illegal?
Intercepting other people's communications without permission is illegal in most countries, under wiretapping, computer misuse or data protection laws. Security testing is legal only on systems you own, or where the owner has given you written permission. Trying it on a café, school or office network you don't manage can lead to criminal charges.
Can a man-in-the-middle attack happen on mobile data?
It's much harder than on Wi-Fi. 4G and 5G make the network prove itself to the phone, so a stranger can't set up a look-alike tower the way they can set up a fake hotspot. The known weak spot is 2G, which doesn't make the phone verify the tower. Vietnamese authorities reported fake 2G base stations sending spoofed text messages in 2023.
Does two-factor authentication stop MITM?
Codes sent by SMS or generated in an authenticator app don't. A fake login page can forward the code to the real site within seconds. Passkeys and FIDO security keys do stop it, because each key is bound to the real domain and refuses to sign in anywhere else.
What is the difference between MITM and phishing?
Phishing tricks you into handing over information yourself, usually through a fake email, text or page. A MITM attack puts the attacker inside a connection you believe is direct, often without any trick on screen. Adversary-in-the-middle phishing mixes the two: a phishing link brings you to a page that stands between you and the real service.
Is sniffing the same as a man-in-the-middle attack?
No. Sniffing is passive: the attacker records traffic that passes on a shared network and changes nothing. A man-in-the-middle attack is active, because the attacker first pulls traffic through their own device and can then alter or block it. On HTTPS, sniffing reveals little beyond domain names and traffic volume.